Hyundai and Kia reported ARAI compliance: what the cybersecurity milestone means
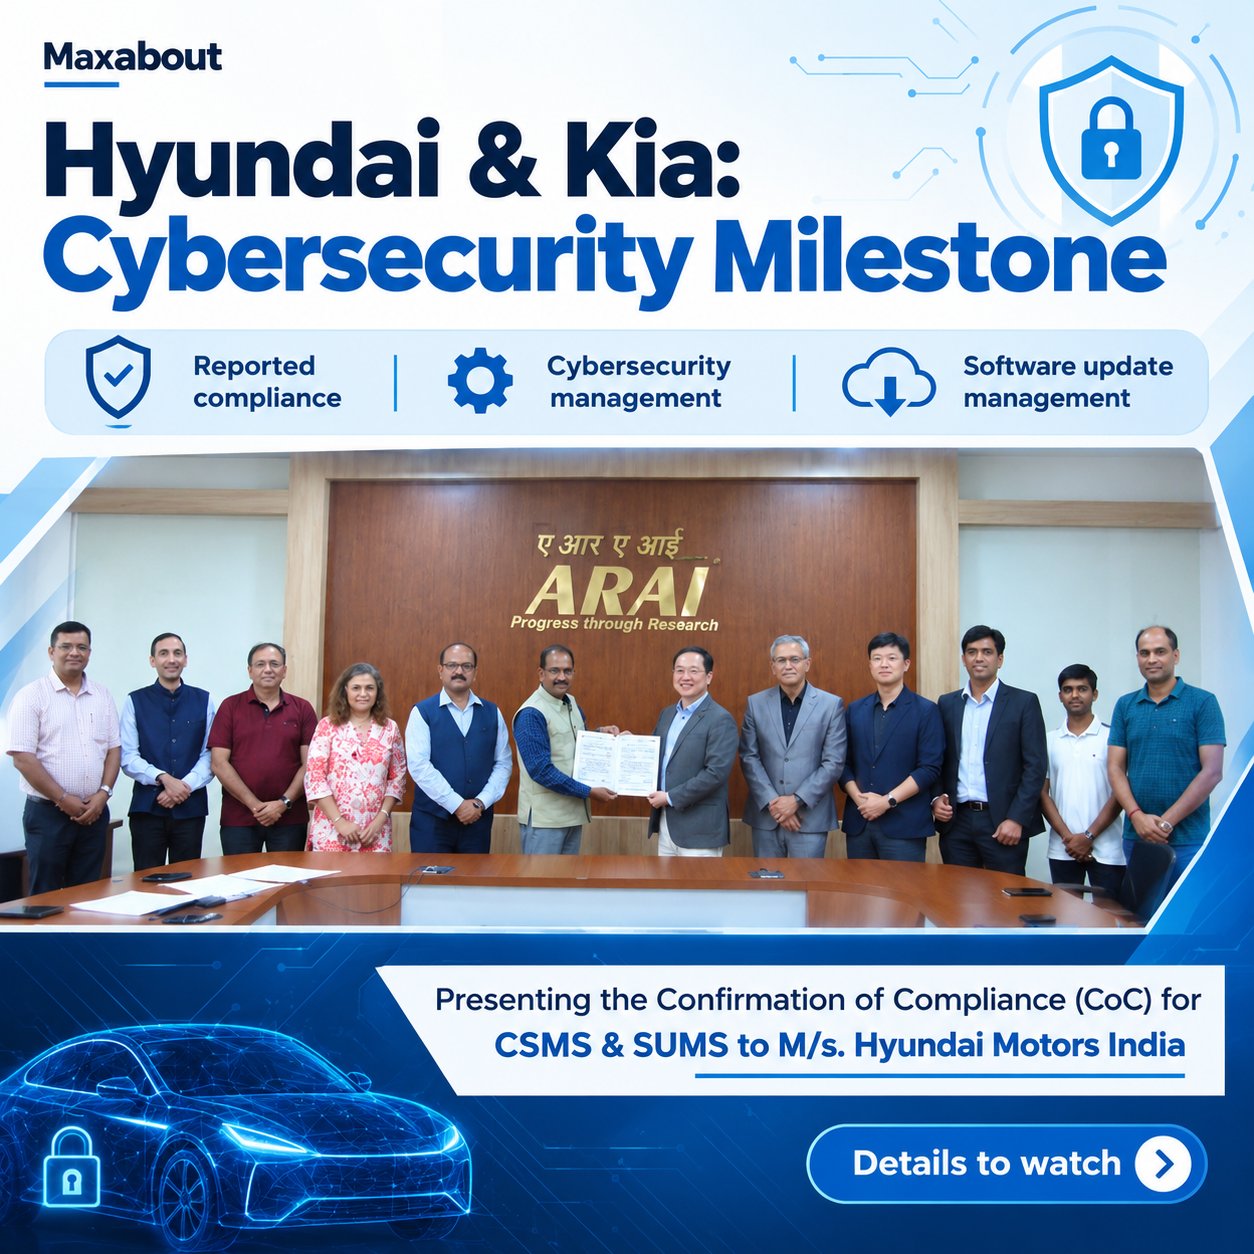
Hyundai Motor India Engineering and Kia India are reported to have received ARAI Confirmation of Compliance certifications concerning cybersecurity and software-update management systems. The report associates AIS:189 with cybersecurity management and AIS:190 with software-update management. The mil...
Hyundai Motor India Engineering and Kia India are reported to have received ARAI Confirmation of Compliance certifications concerning cybersecurity and software-update management systems. The report associates AIS:189 with cybersecurity management and AIS:190 with software-update management. The milestone concerns organisational processes for connected-vehicle electronics and software across product lifecycles; it should not be read as proof that every Hyundai or Kia model has separately received vehicle-level approval.
What has been reported?
The checked account describes compliance for Hyundai Motor India Engineering's Cybersecurity Management System, or CSMS, and Software Update Management System, or SUMS, alongside Kia India. It reports that ARAI representatives presented the certificates to the engineering organisation.
Direct certificate documents, identification numbers, validity dates and the full scope of covered entities or vehicles were not established in the checked material. The news is therefore presented as a reported compliance event, with those details still to be confirmed.
Cybersecurity and updates are related but different
| Reported system | Standard named in the report | Reported focus |
|---|---|---|
| CSMS | AIS:189 | Governance for securing connected-vehicle electronics across the product lifecycle |
| SUMS | AIS:190 | Governance for managing software updates, including over-the-air updates |
A cybersecurity-management process concerns how risks are managed over time. Software-update management concerns the process around changing a vehicle's software. They overlap because updates can address problems, but they are not interchangeable labels for the same function.
What owners should and should not infer
The reported milestone is relevant to the organisation behind connected-vehicle engineering. It does not establish a new feature, a specific update available today, an update-support period or the certification status of a particular model and variant.
It also does not promise that software or electronics can never encounter a security issue. Owners still need model-specific information about update availability, service actions and the support offered for their vehicle. Those details come from the applicable vehicle documentation and official customer communication.
Model coverage: Check which vehicle, model year and system are covered.
Updates: Distinguish an available customer update from a management-system certification.
Support: Ask what support period and channels apply to the exact car.
Documentation: Look for the certificate scope before making model-level conclusions.
FAQs
Does the report certify every Hyundai and Kia car?
That conclusion is not established. The reported event concerns management systems, and model-level applicability needs separate confirmation.
Does this mean a new OTA feature is being released?
No specific customer-facing update or new feature is established by this report.
The Hyundai and Kia compliance report is a meaningful engineering-governance milestone. Its value is clearest when the organisational achievement is kept separate from unverified claims about individual cars, new features or guaranteed security.
Explore the story
Related news
Share your view and join the discussion.
Earn reward points for every comment and get a chance to win ₹1,000 in our weekly lucky draw. Sign in with Google in one tap.
Start the conversation
No one has commented on this article yet. Be the first to share your view.
Want to read more automotive news?
Stay updated with the latest car launches, reviews, and industry insights.
Browse All News