Tata iRA app security advisory: affected versions, fixes and what owners should do
Check Tata iRA 2.0 and iRA.ev affected versions, the corrected releases and the practical update steps owners should take after the security advisory.
Owners using Tata Motors iRA 2.0 or iRA.ev should check their installed app version and complete any pending official update following a High-severity security advisory issued on 4 November 2026. The affected releases are iRA 2.0 version 26.7.3 and earlier, and iRA.ev version 26.7.2 and earlier. Corrected versions are listed below. Tata says mandatory updates had already been rolled out in August and September and that its assessment found no evidence of customer-data compromise. A disclosed vulnerability is a potential weakness; it is not, by itself, proof that a breach occurred.
Which Tata iRA versions are affected?
The two applications serve different groups of Tata owners: iRA 2.0 provides connected services for internal combustion engine vehicles, while iRA.ev serves electric vehicle customers. Check the name of the application as well as its version; the version numbers are not interchangeable.
| Application | Affected versions | Corrected version listed in the advisory | Owner action |
|---|---|---|---|
| Tata Motors iRA 2.0 | 26.7.3 and earlier | 26.8.2 | Check for and install the latest official update. |
| Tata Motors iRA.ev | 26.7.2 and earlier | 26.9.1 | Check for and install the latest official update. |
These are the corrected releases named in the advisory, rather than a claim that no newer version exists. If the official application channel offers a later release, follow the current official update path.
What does the security warning mean?
The advisory describes weaknesses involving credentials embedded in the application package, validation of web content, authentication information appearing in debug logs, and secure-communication configuration. Depending on the weakness and the attack conditions, the potential consequences include exposure of sensitive credentials, user impersonation or unauthorised access to vehicle-related information and application services.
That does not establish that attackers accessed an owner's account or took control of a vehicle. The warning identifies risks that required fixes. It does not announce a confirmed customer-data breach. Owners should treat the update as a practical security action while keeping that distinction clear.
What Tata says it has already fixed
Tata says mandatory updates to iRA 2.0 version 26.8.2 and iRA.ev version 26.9.1 were rolled out in August and September 2026 respectively. That places its stated rollout before the public advisory dated 4 November.
The company says active users have completed the update rollout and that it is contacting remaining customers who have yet to update. It also says its assessment found no evidence of unauthorised access to or compromise of customer credentials, personal information or vehicle-related data. These are Tata's statements about its assessment and remediation, rather than an independent guarantee that every individual phone is up to date.
What owners should check now
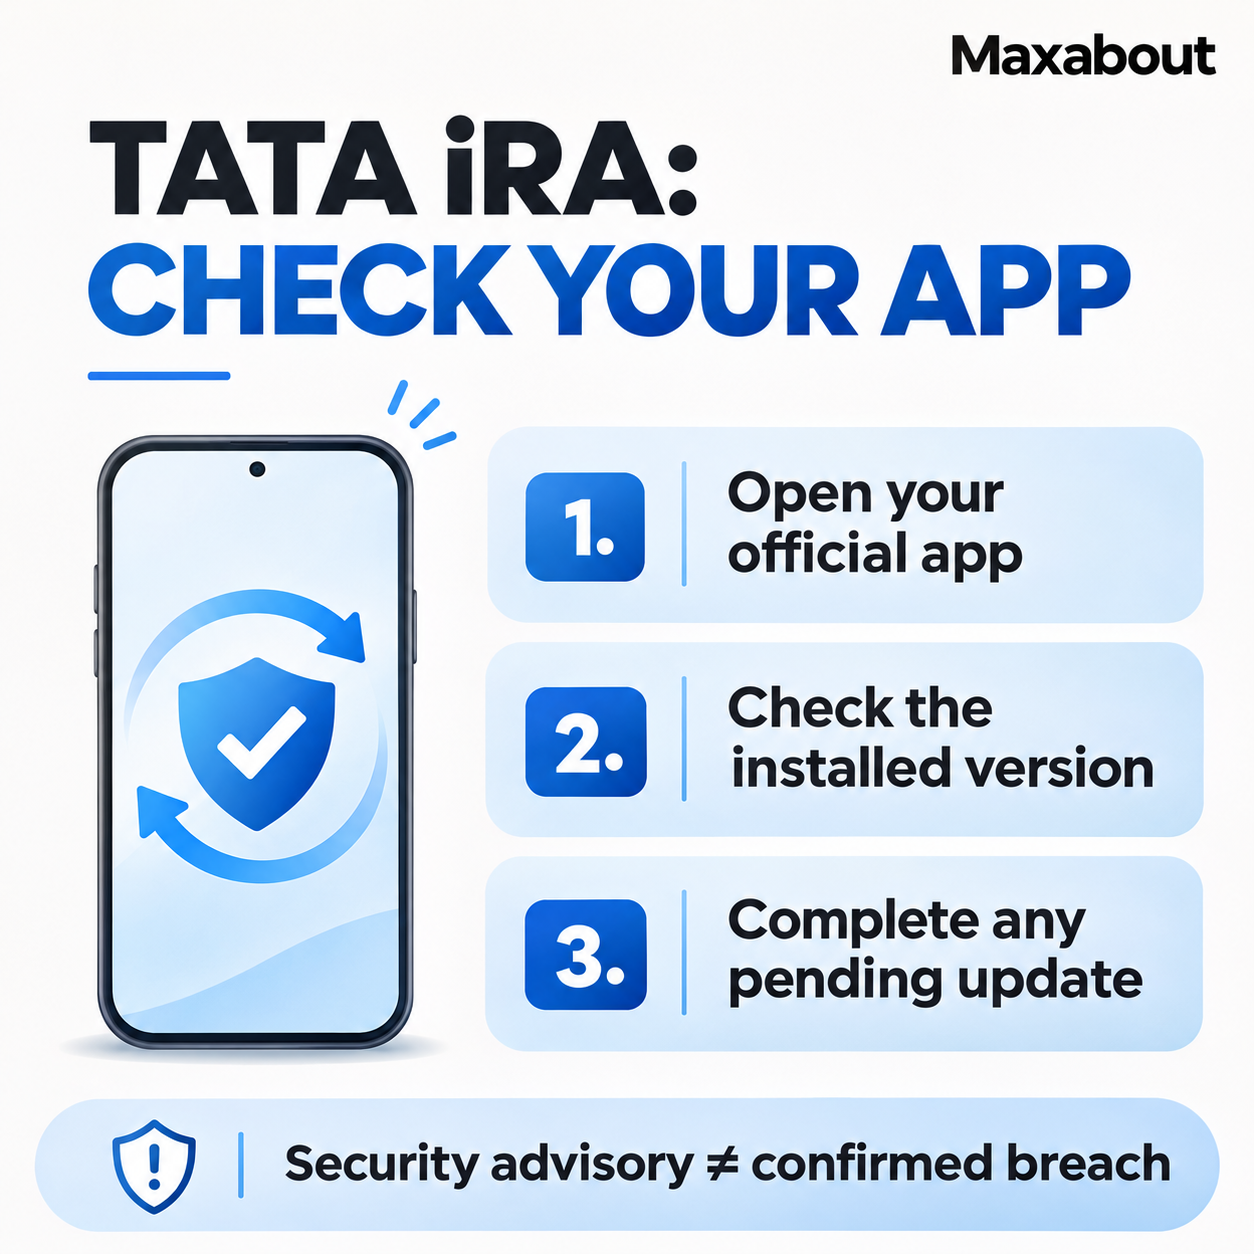
- Identify the right app. Check whether you use iRA 2.0 or iRA.ev.
- Check the installed version. Use the app's available version information or the phone's application details and compare it with the affected releases above.
- Complete pending official updates. Open the genuine app or its official store listing and follow the update process. Avoid update files or login links sent by unknown accounts.
- Confirm the result. Recheck the version after installation. An available update and an installed update are different things.
- Ask for help if it will not update. Use Tata's official customer-support route rather than repeatedly installing unverified packages.
Why this matters for connected-car ownership
Connected-car applications provide access to information such as vehicle status, health monitoring and trip details, as well as connected services. Keeping the app current is therefore part of maintaining the digital access associated with the car. The immediate task is an application update check; the advisory does not establish a mechanical defect or announce a physical vehicle recall.
FAQs
Does the advisory confirm that Tata customer data was stolen?
No. It identifies vulnerabilities and potential impacts. Tata says its assessment found no evidence of compromise; that statement should be kept separate from the existence of the vulnerabilities.
Which corrected versions are listed?
The advisory lists iRA 2.0 version 26.8.2 and iRA.ev version 26.9.1. Check the latest official release available for your application.
Do I still need to check if updates were mandatory?
Yes. Tata distinguishes active users from remaining customers it is contacting. Checking the version on your own phone confirms whether the update is installed there.
The useful response to the Tata iRA security advisory is straightforward: identify the application, check its installed version and complete any pending official update. Keep potential risks, Tata's remediation statement and evidence of an actual incident distinct.
Explore the story
Related news
Share your view and join the discussion.
Earn reward points for every comment and get a chance to win ₹1,000 in our weekly lucky draw. Sign in with Google in one tap.
Start the conversation
No one has commented on this article yet. Be the first to share your view.
Want to read more automotive news?
Stay updated with the latest car launches, reviews, and industry insights.
Browse All News